Updated 2 November 2026: rewritten and checked for Windows 10 and Windows 11.
BitLocker is the drive encryption built into Windows Pro. Switch it on and anyone who takes your laptop, or pulls out its SSD, sees only scrambled data. Out of the box, though, BitLocker uses 128-bit encryption and unlocks itself with the TPM chip, so you never type anything at start-up. That is convenient, but it is not the strongest set-up.
Below is the tweak I use on my own machines: 256-bit encryption plus a PIN before Windows starts. First, a quick look at how BitLocker and the TPM work together, because it explains why the PIN matters so much.
What is the TPM chip?
The TPM (Trusted Platform Module) is a small security chip on the motherboard, or built into the processor (Intel PTT, AMD fTPM). It keeps encryption keys safe and checks that the computer starts up the same way every time. Windows 11 requires TPM 2.0, largely for features like this.
At every start, each step of the boot (the firmware, the Windows boot manager and the start-up files) is measured and recorded in the TPM, one after another. Security people call this the chain of trust. If one link changes, the chain no longer matches.
How BitLocker uses the TPM
BitLocker encrypts your drive with one key and then locks that key with a master key. The master key can be unlocked in a few different ways, called protectors:
- The TPM, which hands the key over only if the chain of trust matches
- A PIN or password that you type at start-up
- A USB key plugged in at start-up
- The 48-digit recovery key, your spare key for when everything else fails
With the default TPM-only setting, the key is released automatically when the start-up looks normal. If something in the chain changes, for example a BIOS update, a changed boot loader or the drive moved to another computer, the TPM keeps the key locked and Windows asks for the recovery key.
Why TPM-only is not the strongest setting
In TPM-only mode the key is released before anyone types anything. A stolen laptop that is switched off will still start Windows up to the login screen, with the drive already unlocked. Security researchers have shown that, with the laptop in their hands and the right tools, an attacker can sometimes catch the key on its way out of the TPM chip (see Pulse Security’s TPM sniffing research) or pull it out of the computer’s memory.
A start-up PIN closes that gap. With TPM + PIN, the chip will not release the key until the right PIN is typed, and it blocks further guesses after too many wrong tries. That is why the PIN is the most important part of my tweak.
My tweak: 256-bit encryption and a start-up PIN
Before you start
- You need Windows 10 or 11 Pro, Enterprise or Education. Windows Home has the simpler “Device encryption” instead, without these settings.
- Find your recovery key first and keep a copy away from the laptop: printed, on a USB stick in a drawer, or in your Microsoft account at aka.ms/myrecoverykey.
- Back up your important files. Turning encryption off and on again is safe, but a backup is always worth having.
Step 1: Choose 256-bit encryption
- Press Windows + R, type
gpedit.mscand press Enter. - Go to Computer Configuration > Administrative Templates > Windows Components > BitLocker Drive Encryption.
- Open Choose drive encryption method and cipher strength (Windows 10 [Version 1511] and later) and set it to Enabled.
- For operating system drives and fixed data drives, pick XTS-AES 256-bit. For USB sticks that must also work on older versions of Windows, Microsoft recommends AES-CBC 256-bit.
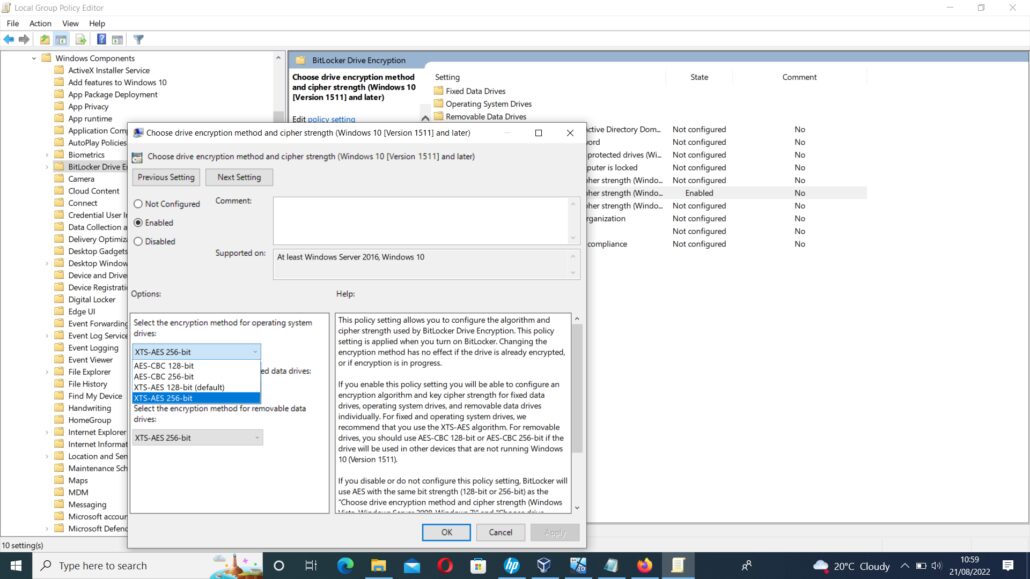
My own settings: Enabled, with XTS-AES 256-bit picked for the operating system drive.
Why “two ciphers”? XTS-AES 256 actually works with two 256-bit keys. One encrypts the data, the other mixes in the position of each block on the disk (that is the “tweak” in XTS). So the same data stored in two different places never looks the same once encrypted.
Is 128-bit unsafe? No. AES-128 is still considered secure, and it is the same strength that protects most Wi-Fi networks. 256-bit simply gives a much bigger safety margin. In real life the weak point is almost always a short or easy PIN, not the encryption itself.
Step 2: Allow enhanced PINs
In the same BitLocker folder, open Operating System Drives, then Allow enhanced PINs for startup, and set it to Enabled. Now your start-up PIN can use letters, capitals, numbers, symbols and spaces, not only digits.
Step 3: Require the PIN at start-up
- Still in Operating System Drives, open Require additional authentication at startup and set it to Enabled.
- If your computer has a TPM (1.2 or 2.0), untick Allow BitLocker without a compatible TPM. You have a TPM, so you do not need this option.
- Set Configure TPM startup PIN to Require startup PIN with TPM.
- Set the other three TPM options to Do not allow.
Step 4: Re-encrypt the drive (the step most people miss)
The new strength only applies when a drive is encrypted. If BitLocker was already on, the drive stays at 128-bit. To check, open Command Prompt as administrator and type:
manage-bde -status C:
Look at Encryption Method. If it still says XTS-AES 128, turn BitLocker off for that drive, wait until decryption reaches 100%, then turn it on again. This can take a few hours, so keep the laptop plugged in and do it at home, not on the move.
Step 5: Set your PIN
When you turn BitLocker on again, Windows asks how to unlock the drive at start-up. Choose Enter a PIN and pick something long that you will remember: up to 20 characters, with capitals, small letters, numbers and symbols. Windows then makes a new recovery key, so save it before you restart.
Tip: before Windows starts, the keyboard can behave like a US keyboard. Symbols such as @ and ” may sit on different keys, and £ may not work at all. Restart once to test your PIN while the recovery key is still to hand.
One more habit: the PIN protects your laptop when it is shut down or hibernating. In sleep mode the drive stays unlocked, so shut the laptop down when you carry it around.
Locked out by BitLocker?
If your laptop suddenly asks for a BitLocker recovery key after a repair, a BIOS update or a new part, do not panic and do not reinstall Windows. If you sign in with a Microsoft account, the key is usually at aka.ms/myrecoverykey. On a work laptop, your IT department usually holds it.
Be careful with anyone who promises to “crack” BitLocker. A drive that is asking for its recovery key cannot be opened without it: not by us, and not by Microsoft. That is the whole point of encryption.
What we can do is repair your laptop without touching your encrypted data, like the ThinkPad X12 charging repair where the customer’s BitLocker-protected files never left the drive. We can also help you find your key, set BitLocker up as described above, and back up your files first.
Computer and laptop repairs in Cambridge and Dagenham
Data recovery
Book a visit
In short
BitLocker with a TPM is already good protection. Switch it to XTS-AES 256-bit, add a long start-up PIN, shut the laptop down when you travel and keep your recovery key somewhere safe. Then a lost laptop is just a lost laptop, not a data leak.